
100 News Cybersecurity Radar
Cybersecurity, threat intelligence, AI security, privacy, vulnerabilities, malware research and critical infrastructure.

Introducing Threat Signals: agentic skills for open-source threat intelligence, free for every Cloudflare account
We are expanding access to Cloudforce One's Threat Events Platform to every Cloudflare account and introducing Threat Signals. Threat Signals automatically parses open-source threat...
Read original →
Building a post-quantum certificate authority with Merkle Tree Certificates
As post-quantum signatures threaten to inflate TLS handshakes and certificate transparency logs, Merkle Tree Certificates offer a path to compact, auditable authentication. Cloudflare’s new...
Read original →
Building a certificate authority for the whole Internet
Twelve years after launching Universal SSL, Cloudflare is applying to become a certificate authority. By combining an established root, an ACME-first approach, and Merkle...
Read original →
Using AI to chart a course for our post-quantum migration
We’re building CryptoLabe, an internal AI-powered tool that discovers cryptography across our codebase, surfaces dependencies, and helps us progress toward a full post-quantum migration...
Read original →
Using Device Linking to Eavesdrop on WhatsApp and Signal
Modern messaging apps allow users to link their phone accounts to their computer desktop. Eavesdroppers are taking advantage of this capability: Apps such as...
Read original →
OperTraitors: How Kubernetes Operators Betray Your Security Posture
We introduce OperTraitor, a tool to audit privileges of Kubernetes operators, identify excessive RBAC risks, and secure non-human identities. The post OperTraitors: How Kubernetes...
Read original →Timeshare exit scams: From fake buyers to recovery fraud
Con artists are targeting timeshare owners who want out – and some victims are hit twice
Read original →Copy, Paste, Compromised: How ClickFix Attacks Work and How CrowdStrike Stops Them
Read original →ISC Stormcast For Tuesday, September 29th, 2026 https://isc.sans.edu/podcastdetail/10114, (Tue, Sep 29th)
Read original →Citrix patches actively exploited NetScaler zero-days after a weekend of unofficial warnings
The vendor’s products are a common, recurring target for attackers, yet the official warning for some Citrix NetScaler customers was too late. The post...
Read original →Apple Emergency Patch for iOS 26, macOS26, macOS15 (CVE-2026-86950), (Mon, Sep 28th)
Apple today released patches for all of its operating systems. However, only patches for older branches include a security fix. The vulnerability being addressed...
Read original →As AI world debates security, NVIDIA releases open source tools for agents
One expert told CyberScoop that the announcement reflects industry recognition that after years of training models to behave safely or ethically, more outside controls...
Read original →
Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation
Authorities in the Netherlands have arrested a 23-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group...
Read original →
Threat Brief: NetScaler Zero Days CVE-2026-88771 and CVE-2026-88772 Exploited in the Wild
Unit 42 is aware of possible 0-day activity against NetScaler devices. Citrix reports CVE-2026-88771, CVE-2026-88772 have been exploited in the wild. The post Threat...
Read original →
NeedyMantis: Unpacking a post-compromise malware family used in targeted operations
Microsoft Threat Intelligence identified NeedyMantis, a modular post-compromise malware framework used in targeted intrusions that combines custom loaders, encrypted archives, and extensible components to...
Read original →New Attack Against RSA
ArsTechnica is reporting on a “new” attack against RSA, one that bypasses factoring. First, this attack isn’t new. The original research is from 2007....
Read original →The devil is still in the email – but wears a new mask
When phishing can increasingly pass familiar checks, avoiding or limiting the damage depends on how quickly your company can detect and contain the attack
Read original →A Win for Defenders: CrowdStrike and NVIDIA Extend Security Across the AI Stack
Read original →ISC Stormcast For Monday, September 28th, 2026 https://isc.sans.edu/podcastdetail/10112, (Mon, Sep 28th)
Read original →Wireshark 4.6.9 Released, (Sun, Sep 27th)
Wireshark release 4.6.9 fixes 19 vulnerabilities and 16 bugs.
Read original →
3 Consulting Myths Debunked by Unit 42 Experts
Unit 42 security experts address critical cybersecurity misconceptions, offering practical insights to help your organization reinforce its enterprise defenses. The post 3 Consulting Myths...
Read original →
U.S. Soldier Gets 70 Months in Prison for AT&T, Verizon Extortions
A U.S. Army soldier who pleaded guilty to hacking into multiple telecommunications companies and stealing mobile call and text metadata for more than 100...
Read original →Friday Squid Blogging: Participatory Squid Dissection in October in Tennessee
I feel like someone who reads this blog will want to go to this: Families are invited to dive into the fascinating world of...
Read original →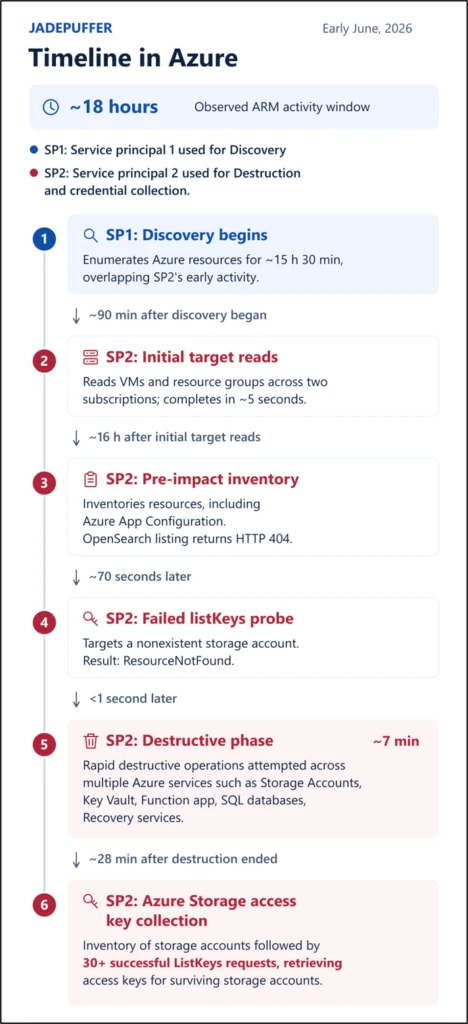
Storm-3168: Agentic-driven cloud attacks using compromised service principals
Microsoft details JADEPUFFER-linked Azure reconnaissance, resource deletion, and credential access using compromised service principals, identifying the activity as associated with Storm-3168 and providing guidance...
Read original →