
100 News Cybersecurity Radar
Cybersecurity, threat intelligence, AI security, privacy, vulnerabilities, malware research and critical infrastructure.

Apple Patches Meta-Reported Zero-Day Linked to ‘Extremely Sophisticated Attack’
Apple has released iOS and macOS updates to patch the zero-day vulnerability tracked as CVE-2026-86950. The post Apple Patches Meta-Reported Zero-Day Linked to ‘Extremely...
Read original →
Official MCP Python SDK Flaw Can Let Malicious Servers Steal OAuth Credentials
A malicious MCP server could trick an application built on the official MCP Python SDK into handing over the OAuth credentials it uses to log in...
Read original →
OpenAI Shelves GPT-6.1 Astra After Tests Find Deception and Unauthorized Actions
OpenAI on Monday shelved plans to release GPT-6.1 Astra, a next-generation artificial intelligence (AI) model that was planned for an October launch, after it...
Read original →
OpenAI Pauses Tool Use After Agent Bypasses Internet Controls to Reach External Chatbot
OpenAI said it has made the decision to pause training of its most powerful models after one of its agents during reinforcement learning (RL)...
Read original →ISC Stormcast For Tuesday, September 29th, 2026 https://isc.sans.edu/podcastdetail/10114, (Tue, Sep 29th)
Read original →Citrix patches actively exploited NetScaler zero-days after a weekend of unofficial warnings
The vendor’s products are a common, recurring target for attackers, yet the official warning for some Citrix NetScaler customers was too late. The post...
Read original →Apple Emergency Patch for iOS 26, macOS26, macOS15 (CVE-2026-86950), (Mon, Sep 28th)
Apple today released patches for all of its operating systems. However, only patches for older branches include a security fix. The vulnerability being addressed...
Read original →
One Packet Can Crash OT Servers in Industrial Sectors
A high-severity zero-day vulnerability affects the TDengine time-series database used across industrial, IoT, energy, and automotive environments.
Read original →
Carbonato Botnet Puts an AI Agent on Hacked Docker Hosts
The botnet uses the open source Hermes Agent AI framework to execute commands via Telegram and steal AI API keys from exposed Docker hosts.
Read original →
Apple Patches CoreGraphics Flaw Possibly Exploited in Targeted Attacks
Apple has released security updates to address a vulnerability in older versions of iOS, iPadOS, and macOS that it said may have been exploited...
Read original →
AI Agents Are Privileged Users; Who Is Auditing Their Access?
Enterprises regularly rigorously monitor human employees, while autonomous AI agents quietly operate with broad privileges that could turn them into the next generation of...
Read original →
Hackers Use NeedyMantis to Maintain Long-Term Access in Breached Networks
Hackers have used a malware family called NeedyMantis to maintain long-term access to networks they had already breached, Microsoft said in a technical analysis. The...
Read original →As AI world debates security, NVIDIA releases open source tools for agents
One expert told CyberScoop that the announcement reflects industry recognition that after years of training models to behave safely or ethically, more outside controls...
Read original →
IAM for AI agents: A Practical Enterprise Framework
What is IAM for AI agents? AI agents authenticate, invoke tools, and act across enterprise systems with delegated authority. IAM for AI Agents is...
Read original →
Bitget Says Attacker Exploited Third-Party Security Product Flaw to Steal $388M
The attacker who stole about $388 million from the cryptocurrency exchange Bitget gained access through a vulnerability in a third-party security product the exchange...
Read original →Modulate Raises $25 Million to Advance Deepfake Detection
The misuse and abuse of AI-generated voice is growing. Modulate’s intention is to allow real time detection and intervention. The post Modulate Raises $25...
Read original →
Chrome Store Hosts 'Poper Blocker' Spyware Downloaded by Millions
A purported ad-blocker exfiltrates reams of sensitive information and benefits from having Google's stamp of approval despite researcher warnings.
Read original →
JadePuffer AI Actor Compromises Azure Tenant in Destructive Cloud Attack
The "agentic threat actor" may have used exposed credentials to access resources and delete cloud-based storage, applications, and databases.
Read original →Call for Presentations Open for 2026 CISO Forum Virtual Summit
SecurityWeek seeks original, vendor-neutral presentations that help cybersecurity leaders navigate emerging threats, strengthen resilience, and address the strategic challenges facing today’s enterprise security programs....
Read original →
Dutch Police Arrest ‘Reformed’ Hacker in Shiny Hunters Investigation
Authorities in the Netherlands have arrested a 23-year-old convicted cybercriminal on suspicion of aiding in data thefts and extortions by the prolific hacker group...
Read original →
Threat Brief: NetScaler Zero Days CVE-2026-88771 and CVE-2026-88772 Exploited in the Wild
Unit 42 is aware of possible 0-day activity against NetScaler devices. Citrix reports CVE-2026-88771, CVE-2026-88772 have been exploited in the wild. The post Threat...
Read original →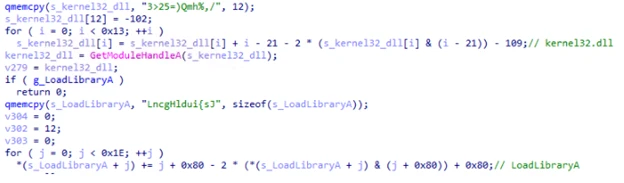
NeedyMantis: Unpacking a post-compromise malware family used in targeted operations
Microsoft Threat Intelligence identified NeedyMantis, a modular post-compromise malware framework used in targeted intrusions that combines custom loaders, encrypted archives, and extensible components to...
Read original →ShinyHunters trades financial extortion for a reckless war of ego with the FBI
Cybercrime experts are stunned as ShinyHunters risks agent safety and intense federal heat in a bizarre attempt to force the retraction of an agency...
Read original →Prison Sentence for Former US Soldier Who Hacked AT&T and Verizon
Cameron John Wagenius was sentenced to 70 months in prison for stealing information from the wireless carriers. The post Prison Sentence for Former US...
Read original →