
100 News Cybersecurity Radar
Cybersecurity, threat intelligence, AI security, privacy, vulnerabilities, malware research and critical infrastructure.
[Virtual Event] Cybersecurity Outlook 2027
Read original →
Secure what’s next: Your guide to Microsoft Security at Microsoft Ignite 2026
This year at Microsoft Ignite, we spotlight our AI-first, end-to-end security platform designed to protect identities, devices, data, applications, clouds, infrastructure, and the AI...
Read original →
As AI Reshapes the SOC Career Ladder, Satisfaction Rises for 91%, but Entry Gets Harder for Nearly Half
New Swimlane research underscores a paradox: While AI detection and response is essential to giving defenders an edge, one in four security pros say...
Read original →
Attackers Exploit Zimbra Flaw to Deploy Web Shells and Harvest Authentication Secrets
Threat actors have weaponized a now-patched security flaw in Zimbra Collaboration Suite (ZCS) to deploy web shells and access mailbox data, according to findings...
Read original →
Attackers Abuse MSP360 to Deploy ScreenConnect in Dual-RMM Phishing Attacks
Microsoft has warned of phishing campaigns distributing an installer for the MSP360 Remote Monitoring and Management (RMM) software under the guise of meeting invitations,...
Read original →
Cisco Warns of Attackers Exploiting Critical Authentication Bypass in SD-WAN Manager
Attackers are exploiting a new critical zero-day flaw in Cisco Catalyst SD-WAN Manager, the system companies use to manage their Cisco SD-WAN networks, Cisco...
Read original →
Russia's Star Blizzard Ditches ClickFix to Widen Phishing Net
The APT actor is using a new tactic, dubbed "RedFlick," against Ukrainian-linked targets such as NGOs, think tanks, and journalists to deploy its CosmicPulse...
Read original →
Attackers Abuse ChatGPT Custom GPTs to Deliver RAT via ClickFix Lures
Threat actors are abusing ChatGPT Custom GPTs to disguise them as legitimate product offerings and direct unsuspecting victims to malicious sites that employ ClickFix...
Read original →
Google: AI Is Changing the Pace and Profile of Vulnerability Discovery
Google’s analysis found that AI-discovered vulnerabilities are more likely to enable remote code execution. The post Google: AI Is Changing the Pace and Profile...
Read original →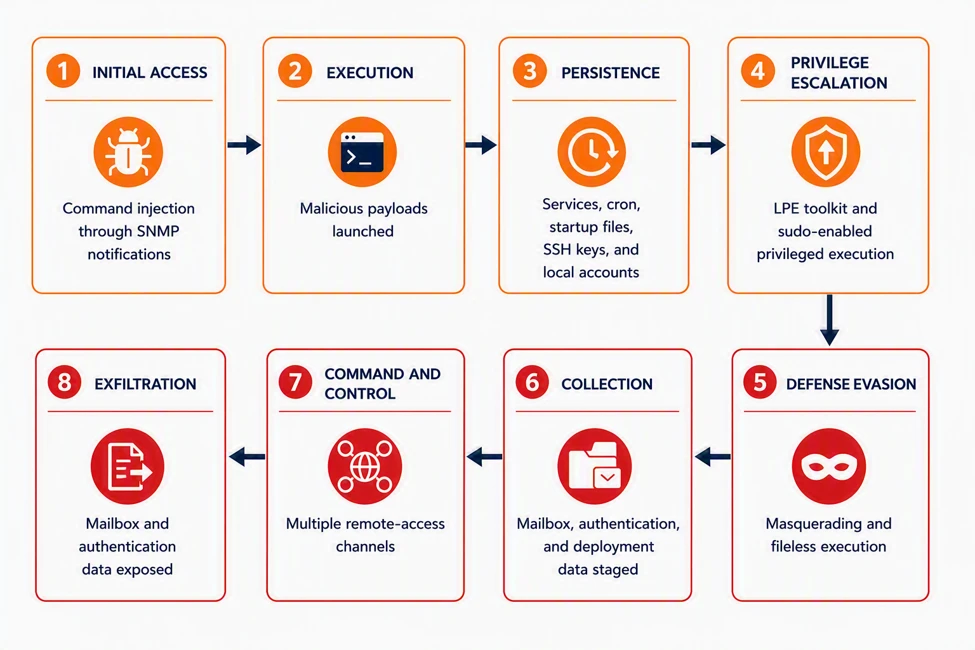
Unauthenticated command injection on internet-facing mail servers: tracking CVE-2026-73570
Microsoft Threat Intelligence examines CVE-2026-73570 exploitation in Zimbra, including observed attack paths, detection opportunities, and mitigation guidance. The post Unauthenticated command injection on internet-facing...
Read original →WatchGuard Patches Critical Fireware OS Code Injection Vulnerability
WatchGuard has rolled out patches for 15 code execution, DoS, authorization, and path traversal bugs in Fireware OS. The post WatchGuard Patches Critical Fireware...
Read original →Government, Finance Orgs Targeted in Weeks-Long NetScaler Zero-Day Attacks
Several security firms have confirmed seeing exploitation of the NetScaler vulnerabilities CVE-2026-88771 and CVE-2026-88772. The post Government, Finance Orgs Targeted in Weeks-Long NetScaler Zero-Day...
Read original →Suspected state-sponsored hackers exploited NetScaler zero-day since early September (CVE-2026-88772)
“Advanced and suspected state-sponsored threat actors” are likely to be behind the initial targeted intrusions that leveraged CVE-2026-88772, one of the two recently disclosed...
Read original →Chrome, Firefox Updates Patch Over 100 Vulnerabilities
Some of the flaws could allow remote attackers to execute arbitrary code or escape the browser sandbox. The post Chrome, Firefox Updates Patch Over...
Read original →
Know Your Enemy: Browser-Based Attack Techniques in 2026
Given that the browser is where business apps are accessed and used, it makes sense that attacks are happening there too. Most breaches today...
Read original →AI coding agents leaked 13,000 internal company screenshots to public GitHub repos
When developers ask AI coding agents to prove that a user interface fix works, some agents have been posting the evidence where anyone can...
Read original →
AI Coding Agents Exposed 13,000 Internal Images, Including Billing Records, on GitHub
AI coding agents asked to share screenshots of code changes for review have put internal company images in public GitHub repositories, security company Glow...
Read original →Anthropic Flags AI Agent Liability Risks as OpenAI Faces Hacking Lawsuit
Attacks by autonomous AI agents are moving out of the lab and into the courtroom, raising unsettled questions about who is liable for what...
Read original →I Want Better Reporting on AI Genie Behavior
AI systems are regularly completing tasks in ways that their prompters don’t want or intend. Some of them are disturbing, and some of them...
Read original →Russian APT Star Blizzard Uses ‘RedFlick’ Infection Chain in Recent Attacks
The state-sponsored group has launched larger-scale phishing campaigns to deploy the CosmicPulse backdoor. The post Russian APT Star Blizzard Uses ‘RedFlick’ Infection Chain in...
Read original →
US-Focused CSuite Phishing Steals Microsoft 365 Sessions and Deploys RMM Tools for Remote Access
ANY.RUN researchers traced a US-focused CSuite phishing campaign across 351 sandbox analyses, with 51% of submissions coming from the United States. Technology, manufacturing, government,...
Read original →OpenInfra Europe’s JFrog Artifactory instance breached, packages potentially compromised
Attackers have compromised a self-hosted JFrog Artifactory instance operated by OpenInfra Europe, the regional hub of the OpenInfra Foundation warned in a security notice...
Read original →ShinyHunters Defiant After FBI Calls on Members to Come Forward
In the wake of a suspected leader’s arrest, ShinyHunters says it never intended to publish data stolen from the FBI. The post ShinyHunters Defiant...
Read original →WaterISAC reckons with range of threats after summer of cyberattacks
Internet-exposed tech, PLCs, outside integrators and inside protections are all factors the water sector’s information sharing and analysis center is watching. The post WaterISAC...
Read original →